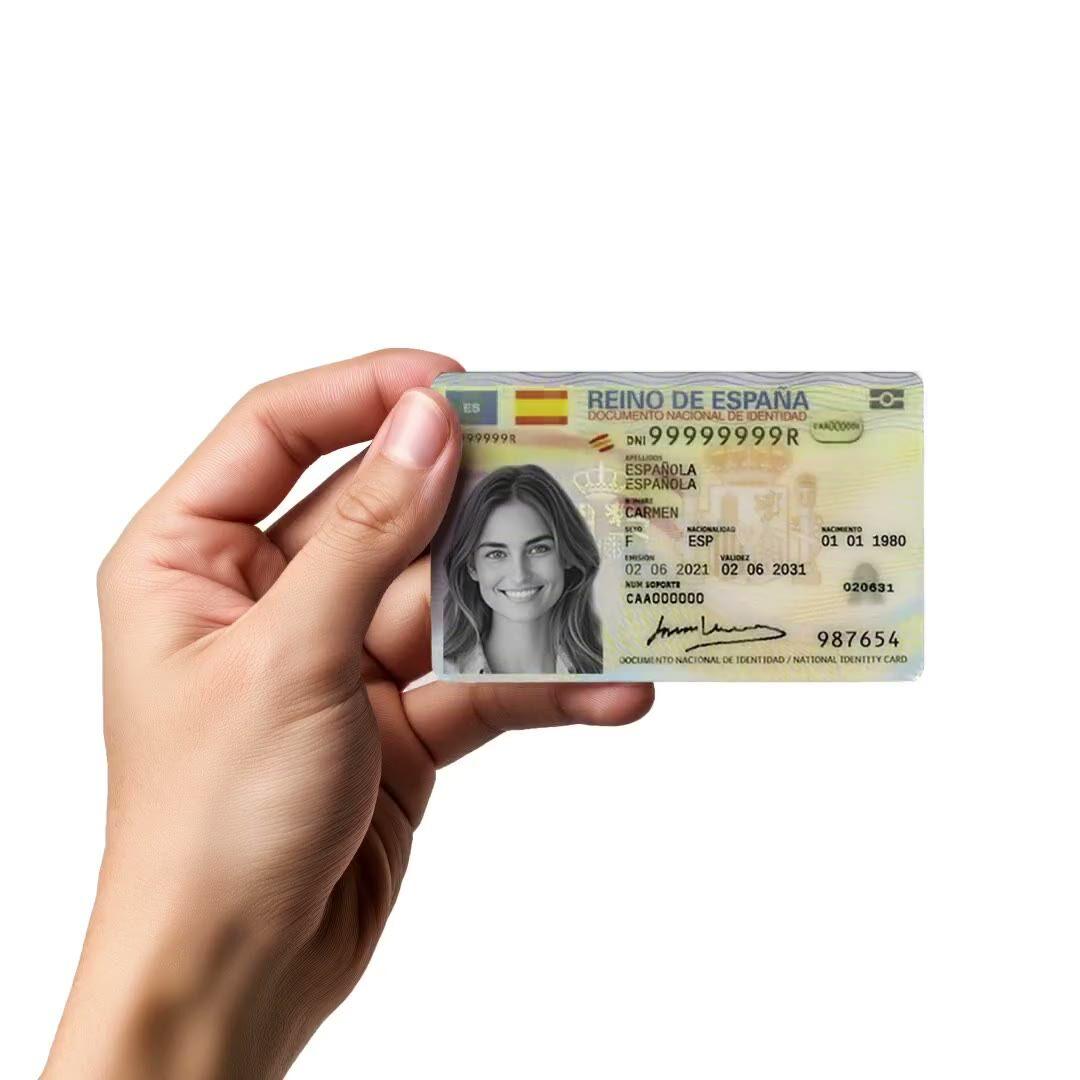
Verify a passport, national ID, driver's licence, or residence permit from any country. 14,000+ documents, sub-2-second verdict, $0.15 per check, 500 free/month.
Spanish DNI, Japanese My Number, UK passport. New documents ship every month,
same $0.15 per check, same verdict shape, same sub-2-second response.
Three ways to verify
One feature. Three methods per country.
Turn on the methods a country actually supports. Every method lands on the same result contract, so your code reads one shape no matter which path the user took.
Method 01
Document capture
Photograph a passport, national ID, driver's licence or residence permit. 220+ countries, 14,000+ documents, a verdict in under two seconds.
Pick the checks you want, ID, liveness, face match, sanctions, address, age, phone, email, custom questions. Drag them into a flow in the dashboard, or post the same flow to our API. Branch on conditions, run A/B tests, no code required.
Integrate
Embed natively with our Web, iOS, Android, React Native, or Flutter SDK. Redirect to a hosted page. Or just send your user a link, by email, SMS, WhatsApp, anywhere. Pick what fits your stack.
User goes through the flow
Didit hosts the camera, the lighting cues, the mobile hand-off, and accessibility. While the user is in the flow, we score 200+ fraud signals in real time and verify every field against authoritative data sources. Result in under two seconds.
You receive the results
Real-time signed webhooks keep your database in sync the moment a user is approved, declined, or sent to review. Poll the API on demand. Or open the console to inspect every session, every signal, and manage cases your way.
Built for developers · Built against fraud · Open by design
Six capabilities. One feature flag. ID_VERIFICATION .
Every capability below is a toggle on the same module. No upsell tiers, no separate SKUs, no add-on calls. Switch them on per workflow in the console, or pass them inline when you call the standalone endpoint.
Passports, national IDs, driver's licences, residence permits. 130+ languages, 50+ scripts (Latin, Arabic, Cyrillic, CJK, Devanagari, Hebrew, Thai, Georgian). New documents ship every month. Per-country subtype controls, accept Indiana Operator and New York Enhanced separately if policy requires it.
Supported documents
Updated this month
Live
220+
Countries
14,000+
Document types
130+
Languages
50+
Scripts
PassportID cardDriver's licenseResidence permit
🇪🇸ES
🇺🇸US
🇧🇷BR
🇩🇪DE
🇲🇽MX
🇮🇳IN
🇫🇷FR
🇬🇧GB
🇯🇵JP
🇳🇬NG
🇦🇪AE
🇸🇬SG
02 · Data extraction
Visual fields, MRZ, and barcode, cross-checked.
Every visual, MRZ (machine-readable-zone), and barcode field extracted in one pass. The three are cross-checked before the response leaves our edge. Inconsistencies surface as warnings so you can route the case to manual review.
Personal data
OCR · MRZ · Barcode
First name
Olivia
Matches with Data provided via API: Olivia
Last name
Roy
Date of birth
28/06/1971
Document type
Passport
Issuing state
Spain🇪🇸
Document number
3EB8726CC6E0F979
03 · Authenticity
Document is real. Portrait is intact. No screen capture.
Template match against the certified database. Hologram and microprint detection. Portrait integrity check. Document liveness defeats four common attack vectors, screen captures, phone photos, printed copies, and portrait substitutions on otherwise-real documents.
Document authenticity
Authentic
Document portrait
Live capture
Similarity 94%
Template match
Hologram detected
Microprint intact
Document liveness passed
04 · Capture quality
Reject blur and glare before they reach review.
Focus, brightness, and resolution scored 0–100 per submission, plus a weighted overall score. Out-of-frame corners and overexposed sides flagged explicitly. Tunable thresholds reject low-quality captures up front so they never reach your manual-review queue.
Capture quality
Capture ready
Hold steady
Overall score
91/100
Focus92
Brightness88
Resolution95
05 · Risk policy
Decide. Review. Approve. Per risk. Per application.
Every risk category, duplicate user, invalid MRZ, data inconsistency, low document liveness, maps to decline, review, or approve. Tune the policy per application, country, and document type. Auto-decline triggers (expired, blocklisted, unsupported) stay enforced regardless of your settings.
Risk policy
5 categories
Risk categoryAction
Duplicated user
Decline
Invalid MRZ
Review
Data inconsistency
Review
Invalid validation
Decline
Low document liveness
Approve
06 · Ongoing KYC
Documents expire. Catch it before the regulator does.
We track expiry on every document you store. When one expires, the user's KYC status flips automatically and we ping you via webhook. No batch job, no quarterly re-onboarding sprint, KYC refresh stays continuous and you stay AML-Directive aligned.
Document monitoring
Auto-tracks expiry · webhook on status change
Live
1,284
Active
47
Expiring soon
9
Expired
Webhook fired · usr_9f01a3c moved to Kyc expired12s ago
Ausr_a8c4f02Passport12 Mar 2027Active
Musr_4d2b6e1ID card08 Jun 2026Expiring
Lusr_9f01a3cDriving license21 Sep 2025KYC expired
Integrate
Two endpoints. Same JSON. Same price.
Create a session when you want our hosted UI to handle capture, or call the standalone endpoint when you already have the image. Both return the same id_verification report.
Paste the block below into Claude Code, Cursor, Codex, Devin, Aider, or Replit Agent. Fill in the my_stack placeholder with your framework, language, and use case. The agent provisions Didit, builds the workflow with ID Verification enabled, wires the webhook, and ships.
didit-integration-prompt.md
# Didit ID Verification — integrate in 5 minutes

You are integrating Didit's ID Verification module into <my_stack>. Follow
these steps exactly. Every URL, header, and enum value below is canonical —
do not paraphrase or "improve" them.

## 1. Provision an account
- Sign up: https://business.didit.me (no credit card required).
- Or provision programmatically: POST https://apx.didit.me/auth/v2/programmatic/register/
  (returns an API key bound to the workspace + application).

## 2. Two integration paths — pick one

### Path A — Workflow Builder (hosted UI)
Best when you want Didit to handle camera, lighting cues, retries,
mobile handoff, and accessibility for you.

1. Create a workflow that contains the ID Verification feature:
   POST https://verification.didit.me/v3/workflows/
   Authorization header:  x-api-key: <your-api-key>
   Body: workflow_label, features array with the single entry
         { feature: "OCR" }   (UPPERCASE — strict enum; "OCR" is the
         workflows-endpoint value for ID Verification, and the only one
         POST /v3/workflows/ accepts for it)

2. Create a verification session for an end user:
   POST https://verification.didit.me/v3/session/
   Body: workflow_id (from step 1), vendor_data (your own user id).
   Response: url (the hosted verification link) — redirect the user to it.

3. Listen for webhook callbacks (see "Webhooks" below).

### Path B — Standalone server-to-server API
Best when you already have the document image (mobile SDK capture, native
onboarding app, reseller pipeline).

POST https://verification.didit.me/v3/id-verification/
Content-Type: multipart/form-data
Body fields:
  - front_image  (required, file)
  - back_image   (optional, file)
  - vendor_data  (optional string, your user id)

Response: JSON report with extracted fields, image quality scores,
warnings array, and the verdict.

## 3. Webhooks (Path A only — Path B returns synchronously)
- Register a webhook destination once via
  POST https://verification.didit.me/v3/webhook/destinations/
  Body: url, subscribed_events: ["session.verified", "session.review_started",
                                  "session.declined", "kyc_expired"]
- Response includes secret_shared_key — store it.
- Every webhook delivery carries an X-Signature-V2 header you MUST verify
  before trusting the payload. X-Signature-V2 signs the CANONICAL JSON, not
  the raw body bytes — that is what makes it survive a proxy or body parser
  that re-encodes the payload. (The legacy X-Signature header is the one
  computed over the raw bytes.) The canonical form is the sender's Python
  json.dumps(sort_keys=True, separators=(",", ":"), ensure_ascii=False)
  after whole-valued floats become ints. Reproduce those bytes EXACTLY —
  do NOT "parse, sort keys, JSON.stringify", which fails in four ways:
    - Numbers come from the wire text, never from parsed doubles: the sender
      signs 1000000000000000129 digit for digit, JSON.parse rounds it. Read
      the body as TEXT (express.text, not express.json()) and re-emit
      integers through BigInt(source). Register the webhook route ABOVE any
      global app.use(express.json()): the first parser to run consumes the
      stream, and the digits are gone before the route sees them.
    - Floats use Python's repr: 1e-05, not 0.00001; 27.0 becomes 27.
    - Keys sort by Unicode CODE POINT, as strings: "10" before "2", and
      U+FF21 before U+1F642 (JavaScript's default .sort() reverses the latter
      because it compares UTF-16 code units).
    - Serialise straight from the sorted entries; never rebuild an object
      first, because JavaScript moves integer-like keys to the front.
  Then HMAC-SHA256 with secret_shared_key, hex-encode, and compare to the
  X-Signature-V2 header in constant time (crypto.timingSafeEqual).
- Freshness comes from the SIGNED body field "timestamp" (Unix seconds):
  reject a delivery whose body timestamp is more than 300 seconds from now,
  and require the X-Timestamp header to equal it. Never check the header
  alone — it is not signed, so a replayed delivery with a rewritten header
  would pass. This is the Node 22 + Express handler, paste it verbatim:

// Your endpoint receives a signed ID Verification payload
const crypto = require("node:crypto"); // ESM: import crypto from "node:crypto"
// X-Signature-V2 = HMAC over the canonical JSON, never the raw bytes. Match the sender byte for
// byte: keys sorted by code point, integers digit for digit, floats in Python's repr.
class Num { constructor(src) { this.src = src; } } // a number as written on the wire, not a double
const num = (s) => { if (/^-?\d+$/.test(s)) return BigInt(s).toString(); const n = +s; // ints stay exact
  if (Number.isInteger(n)) return BigInt(n).toString(); const [m, e] = n.toExponential().split("e"); // 27.0 -> 27
  return +e >= -4 ? String(n) : `${m}e-${String(-e).padStart(2, "0")}`; }; // 1e-05, not 0.00001
const byCodePoint = (a, b) => Buffer.compare(Buffer.from(a), Buffer.from(b)); // UTF-8 order = Python's
const canon = (v) => Array.isArray(v) ? `[${v.map(canon)}]` : v instanceof Num ? num(v.src)
  : v && typeof v === "object" ? `{${Object.keys(v).sort(byCodePoint).map((k) => `${JSON.stringify(k)}:${canon(v[k])}`)}}`
  : JSON.stringify(v);
// Read the body as text: express.json() would round 1000000000000000129 to a double first.
// Register this route ABOVE any global app.use(express.json()): the first parser to run
// consumes the stream, and a body it already parsed has lost the digits the signature covers.
app.post("/webhooks/didit", express.text({ type: "application/json" }), (req, res) => {
  const exact = JSON.parse(req.body, (k, v, c) => typeof v === "number" ? new Num(c.source) : v); // Node 21+
  const body = JSON.parse(req.body);
  const mac = crypto.createHmac("sha256", SECRET).update(canon(exact), "utf8").digest("hex");
  const sig = Buffer.from(String(req.headers["x-signature-v2"] ?? ""));
  // Freshness comes from the signed body timestamp; the header alone is unsigned and replayable.
  const ts = body.timestamp, fresh = String(ts) === req.headers["x-timestamp"]
    && Math.abs(Date.now() / 1000 - ts) <= 300;
  if (!fresh || sig.length !== mac.length
    || !crypto.timingSafeEqual(sig, Buffer.from(mac))) return res.sendStatus(401);
  const { status, decision, vendor_data } = body;
  // status: Approved | Declined | In Review | Expired | Not Finished
  res.sendStatus(200);
});

## 4. Reading the report
Both paths return the same FIELDS, in a different container:
- Path A (session decision + webhook): decision.id_verifications is an ARRAY
  — one entry per ID Verification node in the workflow. Select the entry you
  want by its node_id, never by index and never as a singular object:
      const doc = decision.id_verifications.find(
        (v) => v.node_id === "id_verification_1"
      );
  Every other feature is plural the same way: liveness_checks,
  face_matches, aml_screenings, ip_analyses, nfc_verifications,
  poa_verifications, database_validations.
- Path B (POST /v3/id-verification/): a single id_verification object on the
  response body — this endpoint runs exactly one document.

Each id_verification entry includes:
- status: "Approved" | "Declined" | "In Review" | "Expired" | "Not Finished"
- document_type: "Passport" | "Identity Card" | "Driver's License" | "Residence Permit" | null
- document_number, personal_number
- front_image, back_image, portrait_image (signed URLs, expire in 1 hour)
- date_of_birth (YYYY-MM-DD), age (number)
- expiration_date, date_of_issue (YYYY-MM-DD)
- issuing_state, issuing_state_name (ISO 3166-1 alpha-3 + display name)
- first_name, last_name, full_name
- gender ("M" | "F" | "U"), nationality (ISO 3166-1 alpha-3)
- address, formatted_address, parsed_address (street_1, street_2, city,
  region, postal_code, geometry { lat, lng })
- front_image_quality_score / back_image_quality_score (focus, brightness,
  resolution, overall, each 0-100)
- warnings: Array<{ risk, log_type, short_description, long_description }>

## 5. Hard rules — do not change
- Base URL for /v3/* endpoints is verification.didit.me (NOT apx.didit.me).
- Feature enum is UPPERCASE: OCR (ID Verification), LIVENESS, FACE_MATCH, AML, IP_ANALYSIS.
- Auth header is x-api-key (lowercase, hyphenated).
- Webhook signature header is X-Signature-V2 (NOT X-Signature), and it signs
  the canonical JSON — never HMAC the raw bytes under that header, and never
  canonicalise a parsed object: read the body as text and serialise the
  sender's bytes (see the handler in section 3).
- Webhook freshness is the signed body "timestamp" (300 s window); the
  X-Timestamp header must equal it and is never checked on its own.
- decision.id_verifications is an array; select the node you want by node_id.
- Always verify webhook signatures before trusting payload data.
- Status casing matches exactly: "Approved", "Declined", "In Review",
  "Expired", "Not Finished" (title-cased, space-separated).

## 6. Pricing reference (public)
- Path A bundled in a full KYC workflow: $0.33 per session
- Path B standalone /v3/id-verification/ call: $0.15 per call
- 500 free verifications every month, forever, on every account.

## 7. Verify your integration
- Sandbox starts on signup at https://business.didit.me — no separate flag.
- Test docs: deterministic synthetic IDs returned in sandbox.
- Switch to live: flip the application's environment toggle in console.

When in doubt: https://docs.didit.me/core-technology/id-verification/overview
Compliant by design
Open a new country in one click. We do the hard work.
We open the local subsidiaries, secure the licenses, run the penetration tests, earn the certifications, and align with every new regulation. To ship verifications in a new country, flip a toggle. 220+ countries live, audited and pen-tested every quarter, the only identity provider an EU member-state government has formally called safer than in-person verification.
Identity document types in the certified database.
<2s
End-to-end inference per verification.
$0.15
Per standalone ID check. 500 free every month.
Three tiers, one price list
Start free. Pay as you go. Scale to Enterprise.
500 free verifications every month, forever. Then pay only when a module runs. Custom contracts, data residency, and service level agreements (SLAs) on Enterprise.
Free
$0/ month · no card
For building, testing, and your first users.
Everything you need to start:
500 full KYC verifications every month
ID, liveness, face match, device & IP
200+ fraud signals, blocklist, duplicates
Reusable KYC across the Didit network
Workflow builder, case management, SDKs
AI supportIn-console AI agent, docs, and community.