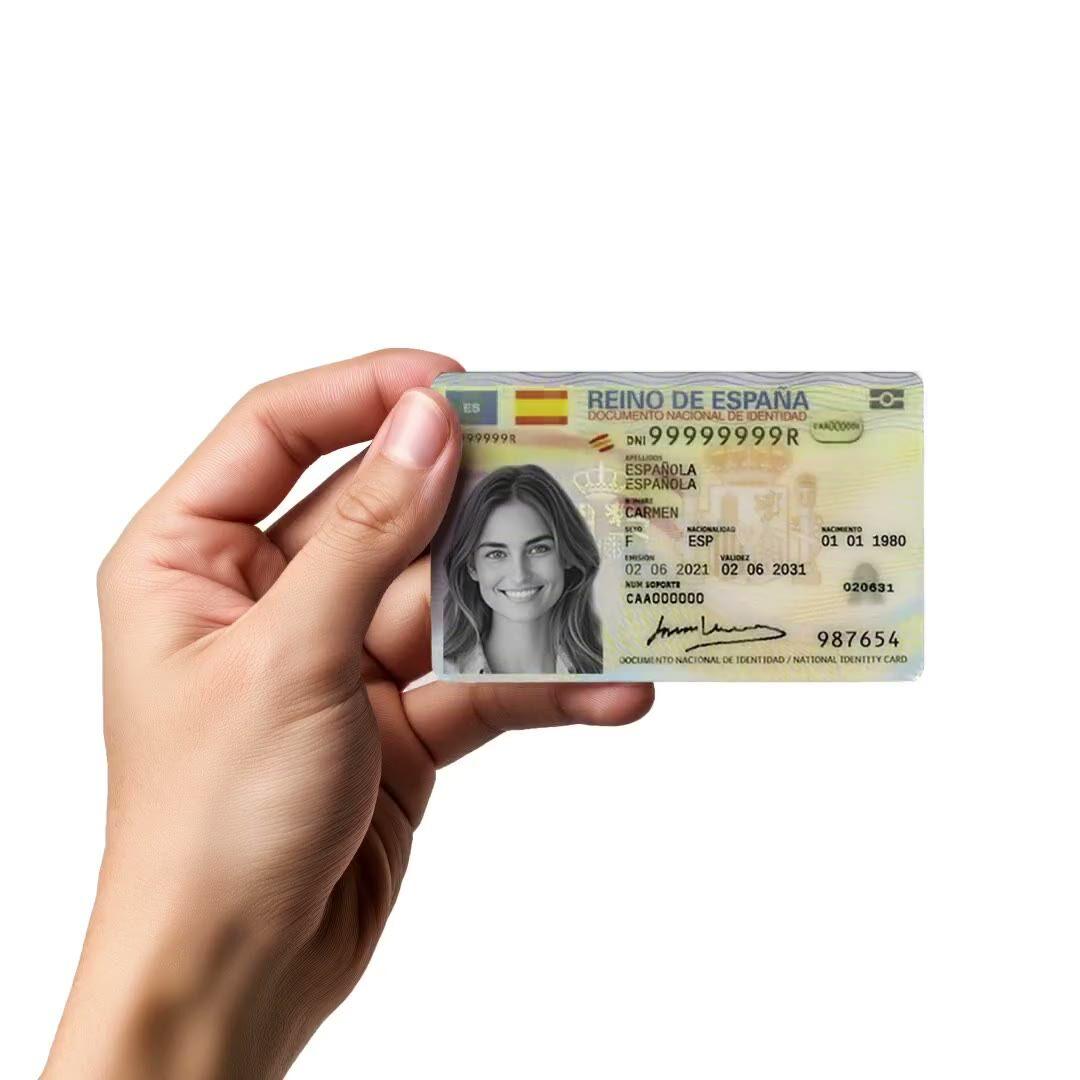
Verifikasi paspor, KTP, SIM, atau izin tinggal dari negara mana pun. 14.000+ dokumen, hasil kurang dari 2 detik, $0.15 per pemeriksaan, 500 gratis/bulan.
Dipercaya oleh 2.000+ organisasi di seluruh dunia.
Cakupan global
14.000+ dokumen. 220+ negara.
DNI Spanyol, My Number Jepang, paspor Inggris. Dokumen baru dirilis setiap bulan,
tetap $0.15 per pemeriksaan, bentuk hasil yang sama, respons kurang dari 2 detik yang sama.
Tiga cara verifikasi
Satu fitur. Tiga metode per negara.
Aktifkan metode yang benar-benar didukung oleh suatu negara. Setiap metode menghasilkan kontrak hasil yang sama, jadi kode Anda membaca satu bentuk tidak peduli jalur mana yang diambil pengguna.
Metode 01
Pengambilan dokumen
Foto paspor, KTP, SIM, atau izin tinggal. 220+ negara, 14.000+ dokumen, hasil dalam waktu kurang dari dua detik.
Dari pendaftaran hingga pengguna terverifikasi dalam empat langkah.
Langkah 01 / 04
01
Buat workflow
Pilih pemeriksaan yang Anda inginkan, ID, liveness, pencocokan wajah, sanksi, alamat, usia, telepon, email, pertanyaan kustom. Seret ke dalam alur di dashboard, atau posting alur yang sama ke API kami. Buat cabang berdasarkan kondisi, jalankan A/B test, tanpa perlu coding.
Integrasikan
Sematkan secara native dengan SDK Web, iOS, Android, React Native, atau Flutter kami. Redirect ke halaman yang di-host. Atau cukup kirim tautan kepada pengguna Anda, melalui email, SMS, WhatsApp, di mana saja. Pilih yang sesuai dengan stack Anda.
Pengguna melewati alur
Didit meng-host kamera, isyarat pencahayaan, serah terima seluler, dan aksesibilitas. Saat pengguna berada dalam alur, kami menilai 200+ sinyal penipuan secara real time dan memverifikasi setiap bidang terhadap sumber data otoritatif. Hasil dalam waktu kurang dari dua detik.
Anda menerima hasilnya
Webhook yang ditandatangani secara real-time menjaga database Anda tetap sinkron saat pengguna disetujui, ditolak, atau dikirim untuk ditinjau. Lakukan polling API sesuai permintaan. Atau buka konsol untuk memeriksa setiap sesi, setiap sinyal, dan kelola kasus sesuai keinginan Anda.
Dibuat untuk developer · Dibangun untuk melawan penipuan · Desain terbuka
Enam kemampuan. Satu feature flag. ID_VERIFICATION .
Setiap kemampuan di bawah ini adalah toggle pada modul yang sama. Tanpa tingkatan upsell, tanpa SKU terpisah, tanpa panggilan add-on. Aktifkan per workflow di konsol, atau teruskan secara inline saat Anda memanggil endpoint standalone.
Paspor, KTP, SIM, izin tinggal. 130+ bahasa, 50+ aksara (Latin, Arab, Kiril, CJK, Devanagari, Ibrani, Thai, Georgia). Dokumen baru rilis tiap bulan. Kontrol subtipe per negara, terima Indiana Operator dan New York Enhanced secara terpisah jika kebijakan mengharuskan.
Dokumen yang didukung
Diperbarui bulan ini
Live
220+
Negara
14,000+
Jenis dokumen
130+
Bahasa
50+
Skrip
PasporKTPSIMIzin tinggal
🇪🇸ES
🇺🇸US
🇧🇷BR
🇩🇪DE
🇲🇽MX
🇮🇳IN
🇫🇷FR
🇬🇧GB
🇯🇵JP
🇳🇬NG
🇦🇪AE
🇸🇬SG
02 · Ekstraksi data
Bidang visual, MRZ, dan barcode, diperiksa silang.
Semua bidang visual, MRZ (machine-readable-zone), dan barcode diekstrak dalam satu proses. Ketiganya diperiksa silang sebelum respons keluar dari sistem kami. Inkonsistensi akan muncul sebagai peringatan agar Anda bisa meneruskan kasusnya ke peninjauan manual.
Data pribadi
OCR · MRZ · Barcode
Nama depan
Olivia
Kecocokan dengan Data yang disediakan via API: Olivia
Nama belakang
Roy
Tanggal lahir
28/06/1971
Jenis dokumen
Passport
Negara penerbit
Spain🇪🇸
Nomor dokumen
3EB8726CC6E0F979
03 · Keaslian
Dokumen asli. Potret utuh. Bukan tangkapan layar.
Pencocokan template dengan database bersertifikat. Deteksi hologram dan microprint. Pemeriksaan integritas potret. Liveness dokumen mengalahkan empat vektor serangan umum, tangkapan layar, foto ponsel, salinan cetak, dan penggantian potret pada dokumen yang sebenarnya asli.
Keaslian dokumen
Autentik
Potret dokumen
Pengambilan langsung
Kemiripan 94%
Kecocokan template
Hologram terdeteksi
Microprint utuh
Liveness dokumen lolos
04 · Kualitas Tangkapan
Tolak blur dan glare sebelum sampai ke peninjauan.
Fokus, kecerahan, dan resolusi dinilai 0–100 per pengajuan, ditambah skor keseluruhan berbobot. Sudut yang di luar bingkai dan sisi yang overexposed ditandai secara eksplisit. Ambang batas yang dapat disesuaikan menolak tangkapan berkualitas rendah di awal sehingga tidak pernah mencapai antrean peninjauan manual Anda.
Kualitas pengambilan gambar
Siap tangkap
Stabil
Skor keseluruhan
91/100
Fokus92
Kecerahan88
Resolusi95
05 · Kebijakan Risiko
Putuskan. Tinjau. Setujui. Per risiko. Per aplikasi.
Setiap kategori risiko, pengguna duplikat, MRZ tidak valid, inkonsistensi data, liveness dokumen rendah, dipetakan ke tolak, tinjau, atau setujui. Sesuaikan kebijakan per aplikasi, negara, dan jenis dokumen. Pemicu penolakan otomatis (kedaluwarsa, masuk daftar hitam, tidak didukung) tetap diberlakukan terlepas dari pengaturan Anda.
Kebijakan risiko
5 kategori
Kategori risikoTindakan
Pengguna duplikat
Tolak
MRZ tidak valid
Tinjau
Inkonsistensi data
Tinjau
Validasi tidak valid
Tolak
Liveness dokumen rendah
Setujui
06 · KYC Berkelanjutan
Dokumen kedaluwarsa. Tangani sebelum regulator yang tahu.
Kami melacak masa berlaku setiap dokumen yang Anda simpan. Ketika ada yang kedaluwarsa, status KYC pengguna otomatis berubah dan kami akan memberitahu Anda via webhook. Tidak ada batch job, tidak ada sprint re-onboarding triwulanan, refresh KYC tetap berkelanjutan dan Anda tetap selaras dengan AML-Directive.
Pemantauan dokumen
Pelacakan otomatis masa berlaku · webhook saat status berubah
Live
1,284
Aktif
47
Segera kedaluwarsa
9
Kedaluwarsa
Webhook terpicu · usr_9f01a3c dipindahkan ke Kyc kedaluwarsa12 detik lalu
Ausr_a8c4f02Paspor12 Mar 2027Aktif
Musr_4d2b6e1KTP08 Jun 2026Akan kedaluwarsa
Lusr_9f01a3cSIM21 Sep 2025KYC kedaluwarsa
Integrasikan
Dua endpoint. JSON yang sama. Harga yang sama.
Buat sesi saat Anda ingin UI yang kami host menangani pengambilan, atau panggil endpoint standalone saat Anda sudah memiliki gambar. Keduanya mengembalikan laporan id_verification yang sama.
Tempel blok kode di bawah ini ke Claude Code, Cursor, Codex, Devin, Aider, atau Replit Agent. Isi placeholder my_stack dengan framework, bahasa, dan use case kamu. Agent akan menyiapkan Didit, membangun workflow dengan Verifikasi ID aktif, menyambungkan webhook, dan langsung deploy.
didit-integration-prompt.md
# Didit ID Verification — integrate in 5 minutes

You are integrating Didit's ID Verification module into <my_stack>. Follow
these steps exactly. Every URL, header, and enum value below is canonical —
do not paraphrase or "improve" them.

## 1. Provision an account
- Sign up: https://business.didit.me (no credit card required).
- Or provision programmatically: POST https://apx.didit.me/auth/v2/programmatic/register/
  (returns an API key bound to the workspace + application).

## 2. Two integration paths — pick one

### Path A — Workflow Builder (hosted UI)
Best when you want Didit to handle camera, lighting cues, retries,
mobile handoff, and accessibility for you.

1. Create a workflow that contains the ID Verification feature:
   POST https://verification.didit.me/v3/workflows/
   Authorization header:  x-api-key: <your-api-key>
   Body: workflow_label, features array with the single entry
         { feature: "OCR" }   (UPPERCASE — strict enum; "OCR" is the
         workflows-endpoint value for ID Verification, and the only one
         POST /v3/workflows/ accepts for it)

2. Create a verification session for an end user:
   POST https://verification.didit.me/v3/session/
   Body: workflow_id (from step 1), vendor_data (your own user id).
   Response: url (the hosted verification link) — redirect the user to it.

3. Listen for webhook callbacks (see "Webhooks" below).

### Path B — Standalone server-to-server API
Best when you already have the document image (mobile SDK capture, native
onboarding app, reseller pipeline).

POST https://verification.didit.me/v3/id-verification/
Content-Type: multipart/form-data
Body fields:
  - front_image  (required, file)
  - back_image   (optional, file)
  - vendor_data  (optional string, your user id)

Response: JSON report with extracted fields, image quality scores,
warnings array, and the verdict.

## 3. Webhooks (Path A only — Path B returns synchronously)
- Register a webhook destination once via
  POST https://verification.didit.me/v3/webhook/destinations/
  Body: url, subscribed_events: ["session.verified", "session.review_started",
                                  "session.declined", "kyc_expired"]
- Response includes secret_shared_key — store it.
- Every webhook delivery carries an X-Signature-V2 header you MUST verify
  before trusting the payload. X-Signature-V2 signs the CANONICAL JSON, not
  the raw body bytes — that is what makes it survive a proxy or body parser
  that re-encodes the payload. (The legacy X-Signature header is the one
  computed over the raw bytes.) The canonical form is the sender's Python
  json.dumps(sort_keys=True, separators=(",", ":"), ensure_ascii=False)
  after whole-valued floats become ints. Reproduce those bytes EXACTLY —
  do NOT "parse, sort keys, JSON.stringify", which fails in four ways:
    - Numbers come from the wire text, never from parsed doubles: the sender
      signs 1000000000000000129 digit for digit, JSON.parse rounds it. Read
      the body as TEXT (express.text, not express.json()) and re-emit
      integers through BigInt(source). Register the webhook route ABOVE any
      global app.use(express.json()): the first parser to run consumes the
      stream, and the digits are gone before the route sees them.
    - Floats use Python's repr: 1e-05, not 0.00001; 27.0 becomes 27.
    - Keys sort by Unicode CODE POINT, as strings: "10" before "2", and
      U+FF21 before U+1F642 (JavaScript's default .sort() reverses the latter
      because it compares UTF-16 code units).
    - Serialise straight from the sorted entries; never rebuild an object
      first, because JavaScript moves integer-like keys to the front.
  Then HMAC-SHA256 with secret_shared_key, hex-encode, and compare to the
  X-Signature-V2 header in constant time (crypto.timingSafeEqual).
- Freshness comes from the SIGNED body field "timestamp" (Unix seconds):
  reject a delivery whose body timestamp is more than 300 seconds from now,
  and require the X-Timestamp header to equal it. Never check the header
  alone — it is not signed, so a replayed delivery with a rewritten header
  would pass. This is the Node 22 + Express handler, paste it verbatim:

// Your endpoint receives a signed ID Verification payload
const crypto = require("node:crypto"); // ESM: import crypto from "node:crypto"
// X-Signature-V2 = HMAC over the canonical JSON, never the raw bytes. Match the sender byte for
// byte: keys sorted by code point, integers digit for digit, floats in Python's repr.
class Num { constructor(src) { this.src = src; } } // a number as written on the wire, not a double
const num = (s) => { if (/^-?\d+$/.test(s)) return BigInt(s).toString(); const n = +s; // ints stay exact
  if (Number.isInteger(n)) return BigInt(n).toString(); const [m, e] = n.toExponential().split("e"); // 27.0 -> 27
  return +e >= -4 ? String(n) : `${m}e-${String(-e).padStart(2, "0")}`; }; // 1e-05, not 0.00001
const byCodePoint = (a, b) => Buffer.compare(Buffer.from(a), Buffer.from(b)); // UTF-8 order = Python's
const canon = (v) => Array.isArray(v) ? `[${v.map(canon)}]` : v instanceof Num ? num(v.src)
  : v && typeof v === "object" ? `{${Object.keys(v).sort(byCodePoint).map((k) => `${JSON.stringify(k)}:${canon(v[k])}`)}}`
  : JSON.stringify(v);
// Read the body as text: express.json() would round 1000000000000000129 to a double first.
// Register this route ABOVE any global app.use(express.json()): the first parser to run
// consumes the stream, and a body it already parsed has lost the digits the signature covers.
app.post("/webhooks/didit", express.text({ type: "application/json" }), (req, res) => {
  const exact = JSON.parse(req.body, (k, v, c) => typeof v === "number" ? new Num(c.source) : v); // Node 21+
  const body = JSON.parse(req.body);
  const mac = crypto.createHmac("sha256", SECRET).update(canon(exact), "utf8").digest("hex");
  const sig = Buffer.from(String(req.headers["x-signature-v2"] ?? ""));
  // Freshness comes from the signed body timestamp; the header alone is unsigned and replayable.
  const ts = body.timestamp, fresh = String(ts) === req.headers["x-timestamp"]
    && Math.abs(Date.now() / 1000 - ts) <= 300;
  if (!fresh || sig.length !== mac.length
    || !crypto.timingSafeEqual(sig, Buffer.from(mac))) return res.sendStatus(401);
  const { status, decision, vendor_data } = body;
  // status: Approved | Declined | In Review | Expired | Not Finished
  res.sendStatus(200);
});

## 4. Reading the report
Both paths return the same FIELDS, in a different container:
- Path A (session decision + webhook): decision.id_verifications is an ARRAY
  — one entry per ID Verification node in the workflow. Select the entry you
  want by its node_id, never by index and never as a singular object:
      const doc = decision.id_verifications.find(
        (v) => v.node_id === "id_verification_1"
      );
  Every other feature is plural the same way: liveness_checks,
  face_matches, aml_screenings, ip_analyses, nfc_verifications,
  poa_verifications, database_validations.
- Path B (POST /v3/id-verification/): a single id_verification object on the
  response body — this endpoint runs exactly one document.

Each id_verification entry includes:
- status: "Approved" | "Declined" | "In Review" | "Expired" | "Not Finished"
- document_type: "Passport" | "Identity Card" | "Driver's License" | "Residence Permit" | null
- document_number, personal_number
- front_image, back_image, portrait_image (signed URLs, expire in 1 hour)
- date_of_birth (YYYY-MM-DD), age (number)
- expiration_date, date_of_issue (YYYY-MM-DD)
- issuing_state, issuing_state_name (ISO 3166-1 alpha-3 + display name)
- first_name, last_name, full_name
- gender ("M" | "F" | "U"), nationality (ISO 3166-1 alpha-3)
- address, formatted_address, parsed_address (street_1, street_2, city,
  region, postal_code, geometry { lat, lng })
- front_image_quality_score / back_image_quality_score (focus, brightness,
  resolution, overall, each 0-100)
- warnings: Array<{ risk, log_type, short_description, long_description }>

## 5. Hard rules — do not change
- Base URL for /v3/* endpoints is verification.didit.me (NOT apx.didit.me).
- Feature enum is UPPERCASE: OCR (ID Verification), LIVENESS, FACE_MATCH, AML, IP_ANALYSIS.
- Auth header is x-api-key (lowercase, hyphenated).
- Webhook signature header is X-Signature-V2 (NOT X-Signature), and it signs
  the canonical JSON — never HMAC the raw bytes under that header, and never
  canonicalise a parsed object: read the body as text and serialise the
  sender's bytes (see the handler in section 3).
- Webhook freshness is the signed body "timestamp" (300 s window); the
  X-Timestamp header must equal it and is never checked on its own.
- decision.id_verifications is an array; select the node you want by node_id.
- Always verify webhook signatures before trusting payload data.
- Status casing matches exactly: "Approved", "Declined", "In Review",
  "Expired", "Not Finished" (title-cased, space-separated).

## 6. Pricing reference (public)
- Path A bundled in a full KYC workflow: $0.33 per session
- Path B standalone /v3/id-verification/ call: $0.15 per call
- 500 free verifications every month, forever, on every account.

## 7. Verify your integration
- Sandbox starts on signup at https://business.didit.me — no separate flag.
- Test docs: deterministic synthetic IDs returned in sandbox.
- Switch to live: flip the application's environment toggle in console.

When in doubt: https://docs.didit.me/core-technology/id-verification/overview
Dirancang untuk kepatuhan
Buka negara baru dengan satu klik. Kami yang mengerjakan bagian sulitnya.
Kami membuka anak perusahaan lokal, mengamankan lisensi, menjalankan pengujian penetrasi, mendapatkan sertifikasi, dan menyelaraskan dengan setiap regulasi baru. Untuk meluncurkan verifikasi di negara baru, cukup aktifkan tombol. 220+ negara sudah aktif, diaudit dan diuji penetrasi setiap kuartal, satu-satunya penyedia identitas yang secara formal disebut oleh pemerintah negara anggota Uni Eropa lebih aman daripada verifikasi langsung.
Jenis dokumen identitas dalam database bersertifikat.
<2s
Inferensi end-to-end per verifikasi.
$0.15
Per pemeriksaan ID mandiri. 500 gratis setiap bulan.
Tiga tingkatan, satu daftar harga
Mulai gratis. Bayar sesuai pemakaian. Skalakan ke Enterprise.
500 verifikasi gratis setiap bulan, selamanya. Setelah itu, bayar hanya saat modul berjalan. Kontrak khusus, data residency, dan service level agreement (SLA) tersedia untuk Enterprise.
Gratis
$0/ bulan · tanpa kartu
Untuk membangun, menguji, dan pengguna pertamamu.
Semua yang kamu butuhkan untuk memulai:
500 verifikasi KYC lengkap setiap bulan
ID, liveness, face match, device & IP
200+ sinyal fraud, blocklist, duplikat
KYC yang bisa digunakan kembali di seluruh jaringan Didit
Workflow builder, case management, SDK
Dukungan AIAgen AI dalam konsol, dokumentasi, dan komunitas.